 Years in Business
 Microsoft Certified Partner
 Client Retention Rate
By Aaron Kane, Founder and CEO of CTI Technology. Last reviewed October 2026.
This checklist covers the IT and security basics every Chicago-area law firm should have in place in 2026. It has 29 checks in seven areas: wire fraud, email and accounts, backups, devices, cyber insurance, AI use, and people. Most firms can review it in about 30 minutes. Any box you can’t check is a gap worth fixing, starting with the wire fraud and email sections.
The list is written for firms with 5 to 150 people, including personal injury, family law, estate planning, real estate, business and employment practices in Chicago and the suburbs.
1. Wire Fraud and Client Payments
Wire fraud is the fastest way a law firm loses money. Criminals break into an email account, watch for a closing or settlement, then send “updated” wire instructions that look real.
- We have a written rule: any new or changed wire instructions are confirmed by phone, using a number we already have on file, never a number from the email.
- Everyone who handles payments, including assistants and paralegals, knows the rule and follows it every time.
- We tell clients at intake that we will never change wire instructions by email.
- Emails from outside the firm are clearly tagged as “External.”
- We get an alert if anyone sets up a rule that auto-forwards or hides email in a firm mailbox.
2. Email and Accounts
- Multi-factor authentication (MFA) is turned on for email, Microsoft 365, practice management software, remote access, and online banking.
- Microsoft 365 security settings require MFA for every user and block sign-ins from unexpected countries or unmanaged devices.
- Administrator accounts are separate from everyday accounts and used only for admin work.
- When someone leaves the firm, their access is removed the same day.
- Shared passwords are kept in a business password manager, not in spreadsheets or sticky notes.
3. Backups and Recovery
- Microsoft 365 email, OneDrive, and SharePoint are backed up by a separate backup service. Microsoft’s built-in retention is not the same as a backup you can restore from.
- Client files and the practice management system are backed up daily.
- At least one backup copy is offline or can’t be changed or deleted, so ransomware can’t reach it.
- We test a restore at least once a quarter and know how long a full recovery would take.
4. Laptops, Phones, and Remote Work
- Every laptop has full-disk encryption turned on.
- Security updates install automatically on computers, phones, and network equipment.
- Every computer runs endpoint detection and response (EDR), not just basic antivirus.
- We can lock or erase a lost or stolen laptop or phone that has firm email on it.
- Remote access uses a secure connection with MFA. Nothing on our network is open directly to the internet for remote desktop.
5. Cyber Insurance Readiness
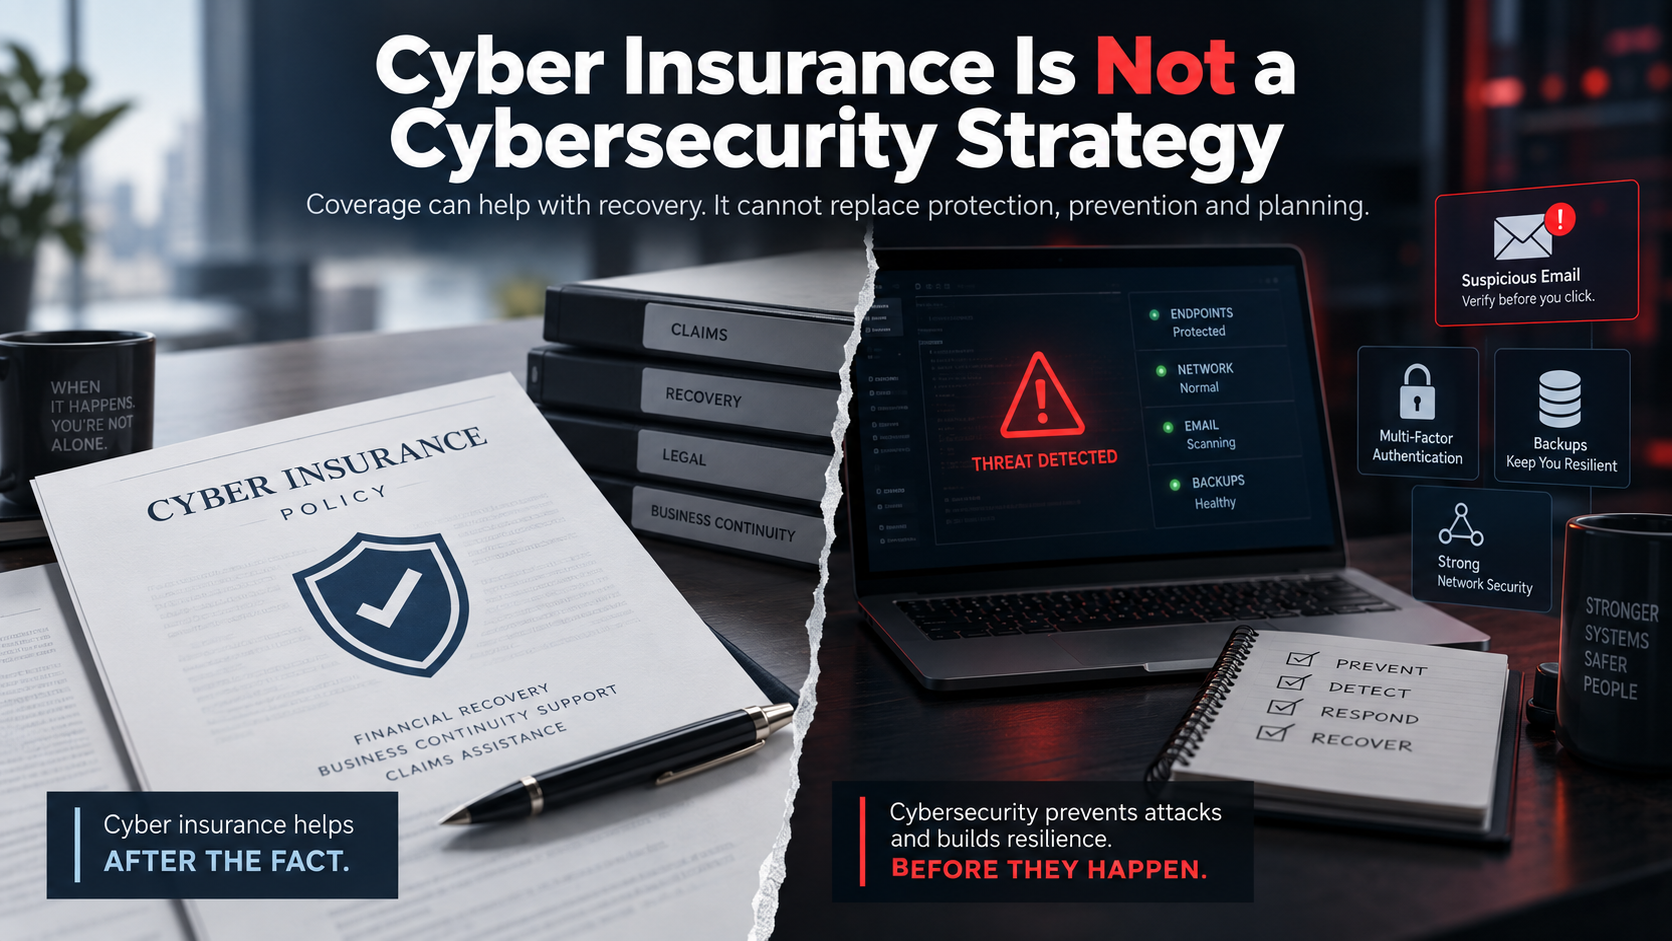
Cyber insurance applications ask detailed questions about your security. A wrong answer can put a claim at risk.
- We keep a copy of our last cyber insurance application and have checked that every answer is still true.
- We can show proof of the controls carriers commonly ask about: MFA, EDR, offline backups, security updates, and staff training.
- We know who to call first if we have a breach: our carrier’s hotline, our IT provider, and our breach counsel.
6. AI Tools and Client Confidentiality
- We have a written AI policy that lists approved tools and what never goes into them, such as client names, case details, and medical records. See CTI’s sample AI policy.
- Staff use business accounts for approved AI tools, not personal logins.
- Before turning on Microsoft Copilot, we cleaned up who can see which files, because Copilot can surface anything a user already has access to.
7. People and Planning
- Everyone gets short security awareness training at least once a year, including practice phishing emails.
- We have a one-page incident plan: who to call, in what order, and how to reach them if email is down.
- We keep a list of vendors that store or access client data, and we know how to get our data back if we leave them.
- Someone at the firm, or our IT provider, reviews this checklist at least once a year.
Why This Matters for Illinois Lawyers
Illinois lawyers have a professional duty here, not just a business reason. Comment 8 to Illinois Rule of Professional Conduct 1.1 makes understanding “the benefits and risks” of technology part of competence, and Rule 1.6(e) requires reasonable efforts to prevent unauthorized disclosure of client information. ISBA Opinion 16-06 adds that this duty continues after you choose a cloud provider, and ABA Formal Opinion 512 (2024) covers generative AI. For a deeper look, read what ABA Rule 1.6 requires from your IT and what Illinois attorneys are required to do about client data.
This checklist is general guidance, not legal advice about your ethics obligations.
How CTI Technology Helps Law Firms
CTI Technology has provided managed IT and cybersecurity for Chicago-area businesses since 2004, from our headquarters in Elgin and our team in Chicago. One flat-rate plan, from $200 to $400 per user per month, covers help desk support, Microsoft 365, backup, and 24/7 threat monitoring and incident response. Our average response and resolution times are both under one hour, and 98.5% of our clients stay with us.
Want a second set of eyes on your answers? Schedule a 15-minute call with Aaron, or call (847) 888-1900 or (312) 922-8600. For a deeper look at law firm IT, read our complete IT guide for Chicago law firms. Still deciding whether your firm needs an outside IT company at all? Download our law firm IT readiness checklist (PDF).
Frequently Asked Questions
What IT security does a law firm need?
A law firm needs multi-factor authentication on email and Microsoft 365, a phone call to a known number before acting on any changed wire instructions, a separate backup of Microsoft 365 and client files with at least one offline copy, encrypted laptops running endpoint detection and response (EDR), 24/7 threat monitoring, a written AI policy, and yearly security training for everyone at the firm. Illinois Rule of Professional Conduct 1.1, Comment 8, and Rule 1.6(e) make reasonable security part of a lawyer’s professional duty.
What is the most important IT security step for a small law firm?
Turn on multi-factor authentication for email and Microsoft 365, and require a phone call to a known number before acting on any changed wire instructions. Those two steps block the most common ways law firms lose money and client data.
How often should a law firm review its IT security?
At least once a year, and any time the firm changes IT providers, adds a new system, or renews cyber insurance.
Is Microsoft 365 backed up automatically?
Microsoft keeps deleted items for a limited time, but that is not a full backup. Most firms need a separate backup service so they can restore email and files after ransomware, a mistake, or a former employee deleting data. CTI’s plans include 250GB of automated Microsoft 365 backup.
Can lawyers use AI tools like ChatGPT or Copilot with client information?
Only with care. Use business accounts with approved tools, follow a written AI policy, and never put confidential client details into personal accounts. ABA Formal Opinion 512 explains the ethics duties that apply.
Aaron Kane
Why Is CTI Technology The Best Choice For IT Services In The Chicagoland Region?

“Great pricing, even better service. Highly recommended!”
Great pricing, even better service. Highly recommended!”
Guido Arquilla

“Great IT company for our business! Highly recommended.”
“Great IT company for our business! Highly recommended.”
Brian Coli
“CTI is a great company and I would not trust my IT services to anyone else.”
CTI is a great company and I would not trust my IT services to anyone else.
Jenny Wagner
CTI Technology Tips & Articles